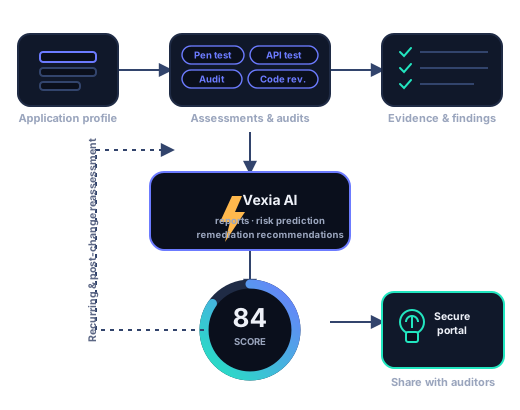
Keep an application's assessments, audit evidence, findings, and remediation
history together in Vexia IQ. Vexia AI can draft reports, project risk trends from the
recorded assessment history, and suggest which findings to address first.
Centralize the whole application security lifecycle.
Register each application and
keep a complete security and compliance profile — name, business purpose, owner,
environment, type, technology stack, URLs, APIs, repositories, deployment details,
criticality, and data classification. Every assessment, audit, document, finding, and
report then lives against that one record.
A structured audit history. Assessments, evidence, and reports stay attached to the application — not scattered across email, shared drives, and chat.
Custom assessment workflows. Build them from your internal security policies, regulatory requirements, customer requirements, or industry standards.
Traceable from requirement to verification. Every audit requirement links to the response, evidence, finding, risk, remediation, and final validation behind it.
Vexia AI on top. Findings and evidence become a drafted report, a predicted risk trajectory, and ranked remediation recommendations.
Run the scenario that fits — a full assessment, a targeted test, an internal audit,
or a customer-driven review — each with its own customizable workflow.
Every document, attached to the application it proves.
A structured place for security and technical documentation — each file stays
associated with its application and assessment, building a real audit history.
Penetration tests and findings, tracked to closure.
Record testing activity directly against an application and follow every finding from
discovery through remediation and validation.
Each assessment captures
Scope, testing methodology, testing dates, testing team, application URLs, APIs and endpoints, and testing environments.
Each finding captures
Severity, business impact, technical impact, proof of concept, remediation recommendations, evidence, retest results, and final status.
Compliance & audit
A traceable line from requirement to verification.
Build assessments from security frameworks, standards, internal controls, or
organization-specific requirements, and customize the questions per application and audit type.
Vexia IQ calculates a security and compliance score from configurable assessment
criteria, so security and management teams get a clear view of application risk without
reading every document.
84SCORE
Roll-up across the whole application portfolio, or drill into a single assessment to see
exactly which findings and gaps are moving the number.
Security & compliance
Overall security score, compliance score, and risk score per application.
Findings
Critical findings, high-risk findings, and open findings at a glance.
Readiness
Remediation progress, assessment status, evidence completeness, and audit readiness.
Collaboration
Built for internal and external audit.
Give each stakeholder exactly the access their review needs — and nothing more.
Internal audit
Security, compliance, engineering, and risk teams run assessments and keep a complete audit trail in one workspace.
External audit
Share selected application information and evidence with external auditors — controlled access to the specific application, assessment, evidence, or report, not your whole environment.
Vendor audit
Assess software provided by vendors. A vendor gets controlled access to submit information, documentation, security reports, and remediation evidence.
Report sharing
Share results without losing control of the file.
Download & share
Generate a professional security or compliance report and send it securely to the customer, auditor, or vendor.
Secure assessment portal
Generate a unique, secure URL for external stakeholders instead of emailing sensitive attachments.
A complete audit trail: who created an assessment, submitted responses, uploaded evidence,
reviewed findings, changed results, approved an assessment, or accessed shared information
— and when reports were generated, evidence updated, and remediation completed.
Continuous assurance
Security posture over time, not a one-time snapshot.
Vexia IQ keeps the historical security posture of each application, so you can compare
assessments over time and see where risk changed. Schedule recurring work:
Annual application auditsPeriodic penetration testingCompliance reassessmentsPost-release assessmentsVendor reassessmentsRemediation verificationReviews after major application changes
Vexia AI
AI that does the write-up, the forecast, and the triage.
The AI layer works on what is already in the record — responses, findings, and
evidence — so its output is grounded in the assessment, not generic advice.
Report generation
Drafts a professional security or compliance report from the assessment's responses, findings, and evidence — ready for review before it goes out.
Risk prediction
Projects how an application's risk and audit readiness will trend, based on open findings, remediation pace, and its assessment history.
Remediation recommendations
Ranks findings by real risk and recommends what to fix first, with rationale and the affected controls called out.
One application. One security record.
Tell us how many applications you manage and which audits you run, and we'll set up a walkthrough of Vexia IQ.